Metrics, logs and traces on one timeline, stored in your own cluster and read by your
browser directly. Your telemetry never passes through our servers.
OpenTelemetry in · Kubernetes · read-only MCP for your agents
Our own Poet, live
drag to zoom · double-click back
Reading our own Poet…
Your data stays home.
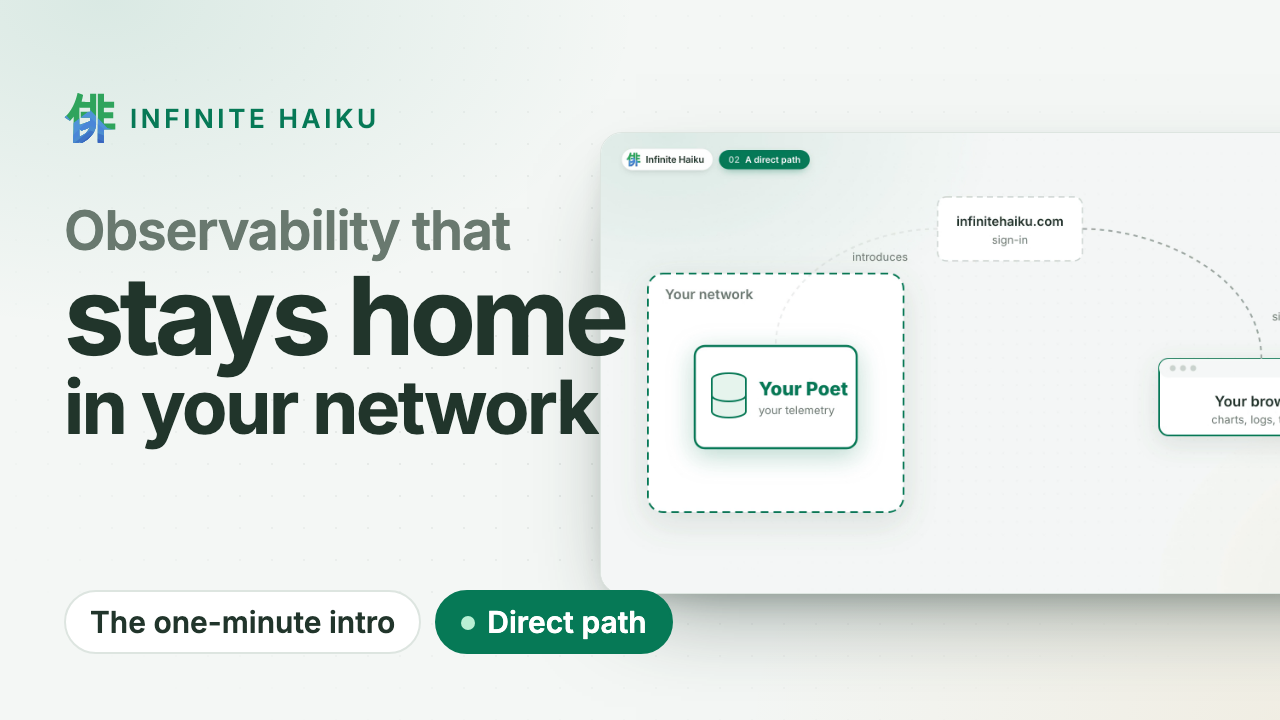
The datastore runs in your Kubernetes cluster or on your Linux machines. We sign you in and introduce your browser
to it; the data goes straight to you over an encrypted channel. No egress bill to ship telemetry
out, and nothing at our end to leak.
Walk into the timeline.
Every series of a service at once, drawn on your GPU. Zoom in and the detail follows; open a
request and see its log lines and the change behind it. Missing data is shown as missing, never
as zero.
Your agents investigate.
A read-only door (MCP) lets the coding agent you already use search, follow a request and read
the same numbers as your charts. No vendor AI, no per-investigation fee.
How it works
1A Poet in your cluster. Our datastore runs where your services run and
takes their OpenTelemetry. Read-only, one namespace.
2You sign in at infinitehaiku.com. Our web service checks who you are and
introduces your browser to your Poet. That is all it sees.
3Your browser talks to your Poet directly. An encrypted peer-to-peer
channel (WebRTC). The numbers never pass through our servers.
Infinite Haiku in one minute · plays from YouTube (youtube-nocookie.com)
Proof, not promises
Measured: 500,000 tasks from 200 workers over five hours, drawn at
1.1 ms of CPU per frame.
This site's own requests, live: the same public view you can give your customers.
Alerts in your network. Evaluated inside your own Poets.
Public status pages. Share a live dashboard without sharing access.
Kernel faults on the timeline. Memory errors, silent out-of-memory kills and disk errors, per node.
Flat CHF 5 per user account and month. Nothing per gigabyte, host or event.
Don't trust us: watch it yourself. Your Poet shows every connection and its bytes, peer to peer or to us. See how
Join the free pilot.
Expert help on your systems. Leave anytime: delete the Poet, one command.
Once we open to the public: two months free, then a flat CHF 5 per user account and month. How the pilot works ·
Security
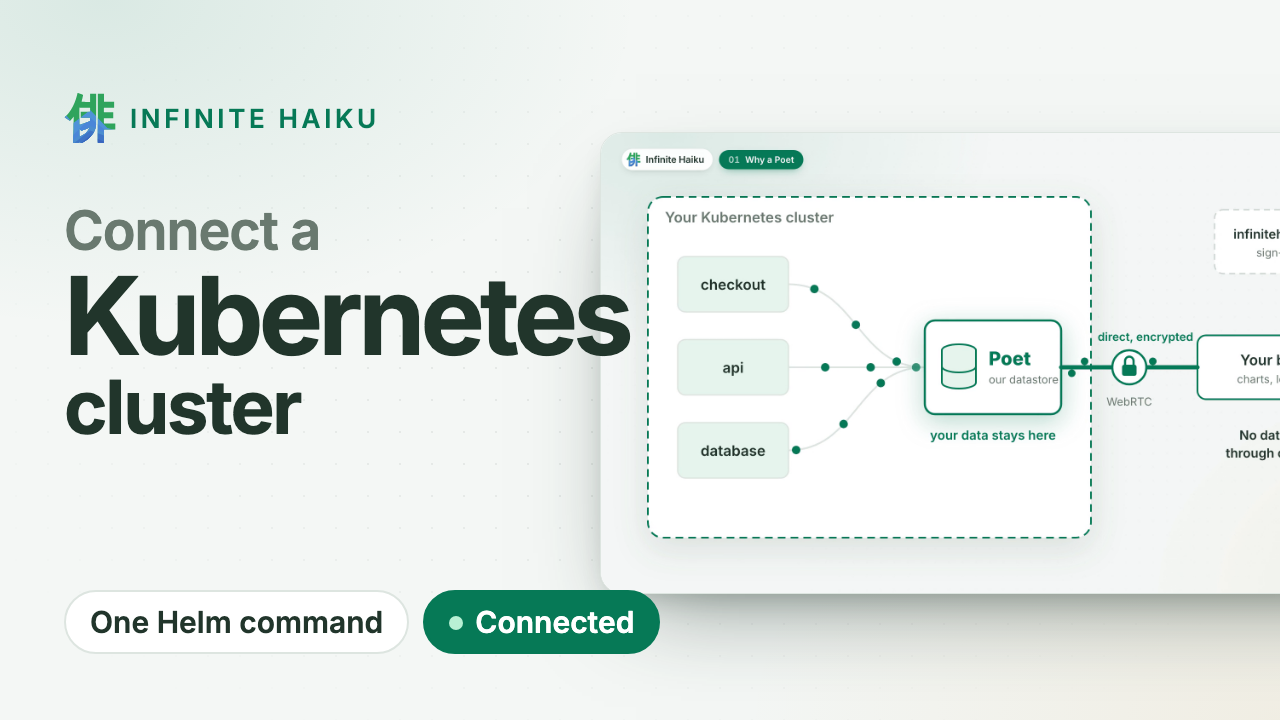
One command installs the Poet, our datastore, and the Kubernetes Muse, our collector, in one pod. Your browser reads the Poet over a direct, encrypted WebRTC connection: no data passes through our servers; we only handle sign-in.
Connect a Kubernetes cluster (1 min) · plays from YouTube (youtube-nocookie.com)
Name your cluster. Sign in at https://infinitehaiku.com as an organisation admin, open Access › Clusters, pick A Kubernetes cluster and enter a name such as prod-eu-1. You get the cluster’s token and the command with your organisation, your cluster and the token filled in.
Paste it in a shell where kubectl and helm reach the cluster. It saves the token to a file only you can read, installs the chart, waits for the pod and removes the file.
Watch it connect. The cluster turns Connected as soon as the Poet starts; the wait is pulling two images and binding the volume. The Muse reads the cluster at once, then every 5 seconds, so your nodes, namespaces and pods follow right after, for everyone in your organisation.
<version> is the newest published chart; Kabuki’s command fills it in.
Without --version Helm installs the newest chart too.
The defaults fit a standard node. Add a flag only if you need it:
Flag
When
--set relayOnly=true
Your cluster may not send UDP to any address: every session goes through our relay (a little more latency)
--set storageClass=<class>
You want a StorageClass other than your default (the volume is 10Gi)
--set image.registry=<mirror>
Your nodes cannot pull from ghcr.io: your mirror’s host, same paths and digests (example)
--set intake.expose=true
Your applications send OpenTelemetry to the Poet (below)
The ids are passed with --set-string, so an id made of digits stays text. No Helm in the cluster, or a policy review first? Install with plain YAML. Flux, a mirror, a pull secret and more: install examples.
OpenTelemetry
With --set intake.expose=true, applications in the cluster send traces,
metrics and logs to the Poet with any OTLP/HTTP exporter. Only namespaces
you label may reach it, on that one port, and every request needs the
Poet’s intake token:
kubectl label namespace shop infinitehaiku.com/send-telemetry=true
kubectl -n infinite-haiku get secret ih-client -o jsonpath='{.data.intake-token}' | base64 -d   # the intake token
Keep the token in a Secret of the sending namespace. An OpenTelemetry
Collector works the same way, with its otlphttp exporter.
Send to an existing Poet
A cluster that needs no datastore of its own runs only the Kubernetes Muse
and sends to a Poet you already have: no volume, no token of ours. In
Access › Clusters, name the cluster and pick Send to an existing
Poet; the screen fills in this command:
The Poet’s address is HTTPS: a Linux Poet’s intake on 4443
(HTTPS intake), or a Kubernetes
Poet with intake.expose=true behind your own TLS ingress (label the
ingress controller’s namespace as above). Another port than 443 or
4443: add --set poetPort=<port>. A private certificate: add
--set-file poetCa=<its CA file> (kept in the Muse’s Secret); without
it the Poet’s certificate must be publicly trusted.
The intake token is the Poet’s: on a Kubernetes Poet, the kubectl get secret line above (run against the Poet’s cluster); on a Linux
Poet, its intake token file.
What gets installed: one Deployment ih-k8s-muse, the same
read-only ClusterRole, a Secret with the token (and the CA, when
given). Egress only: your API
server, DNS and the Poet.
Remove it with helm uninstall infinite-haiku-muse -n infinite-haiku.
Update
Your settings and the token stay; your data stays on its volume:
Without --version Helm upgrades to the newest chart; add
--version <version> to pick one (the newest is the one Kabuki’s
Access › Clusters command shows). A Muse-only install upgrades the
same way: helm upgrade infinite-haiku-muse oci://ghcr.io/infinitehaiku/charts/infinite-haiku-muse -n infinite-haiku --reuse-values.
If you installed under another release name or namespace, helm list -A | grep infinite-haiku shows them; use them in place of infinite-haiku and
-n infinite-haiku above.
Kabuki marks a Poet that runs an older version on Updates and on the
Poet’s own page. An older Poet is updated; Kabuki does not keep older
versions of itself to open it.
Your data was only in your own volume, so that is all it takes to leave. During the pilot there is nothing to cancel; later, uninstalling and cancelling stay separate (leaving).
Then revoke the cluster’s token (poet <cluster>) in Access › Tokens. Your data lived only in the deleted volume.
What you need
Kubernetes 1.25 or later (linux/amd64 or linux/arm64), Helm 3, and the right to create a namespace and one read-only ClusterRole.
The connections below, all opened from inside the cluster; no Service is exposed to the outside.
To
Port
Why
infinitehaiku.com
443 TCP
Registration and signalling
turn.infinitehaiku.com
3478 TCP and UDP, 49160–49999 UDP
Our relay, when no direct path exists
Any address
UDP
Direct WebRTC to your users’ browsers (or use relayOnly)
ghcr.io
443 TCP
The images (or use image.registry)
Your API server and cluster DNS
443/6443 TCP, 53
The Muse reads the cluster
What gets installed
Object
What it does
Pod ih-poet-0
The Poet (our datastore) and the Kubernetes Muse (the collector), side by side
Volume state-ih-poet-0, 10Gi
Your data. It stays in your cluster
Secret, ConfigMap
The token and your settings
ServiceAccount, ClusterRole
Read-only: get, list, watch of pods, nodes, namespaces, events and workloads. Never Secrets, never a write
NetworkPolicies
No ingress; egress only as listed above
Service ih-poet-intake
Only with intake.expose=true: port 4318 for the namespaces you label
No Ingress or LoadBalancer. Every container runs non-root with a read-only filesystem and no capabilities (the restricted Pod Security Standard); we never get access to your cluster.
Troubleshooting
You see
Do this
ErrImagePull
Allow ghcr.io, or add --set image.registry=<mirror>
Pod Pending
kubectl -n infinite-haiku describe pod ih-poet-0: no default StorageClass (add --set storageClass=) or no room on the nodes
Access › Clusters stays on “Waiting for the Poet to register…”
kubectl -n infinite-haiku logs ih-poet-0 -c poet: allow outbound 443 to infinitehaiku.com; a refused token means connect again with a new one
Connected, but the cluster does not open
WebRTC cannot get through: allow UDP out or the TURN ports, or reinstall with --set relayOnly=true
To change a setting later, see upgrading. Need help? Send us the output of kubectl -n infinite-haiku describe pod ih-poet-0 and the pod’s logs; they contain no secret.
The images are for authorised pilots only. The terms are in /LICENSE inside each image, the third-party licences in /THIRD-PARTY-NOTICES.
Welcome back
No account yet? Write to us: during the pilot we set up your organisation with you.